
Sonar runs a full stack of autonomous AI agents on top of its code verification platform: Gitar AI Code Review autonomously reviews pull requests, fixes issues, and keeps committing until the build passes; the SonarQube Remediation Agent works in the background clearing technical debt and opens verified, ready-to-merge pull requests on its own; and the Hunter Agent is a dedicated AI security agent that hunts for logic flaws rather than just pattern-matching known vulnerability signatures.
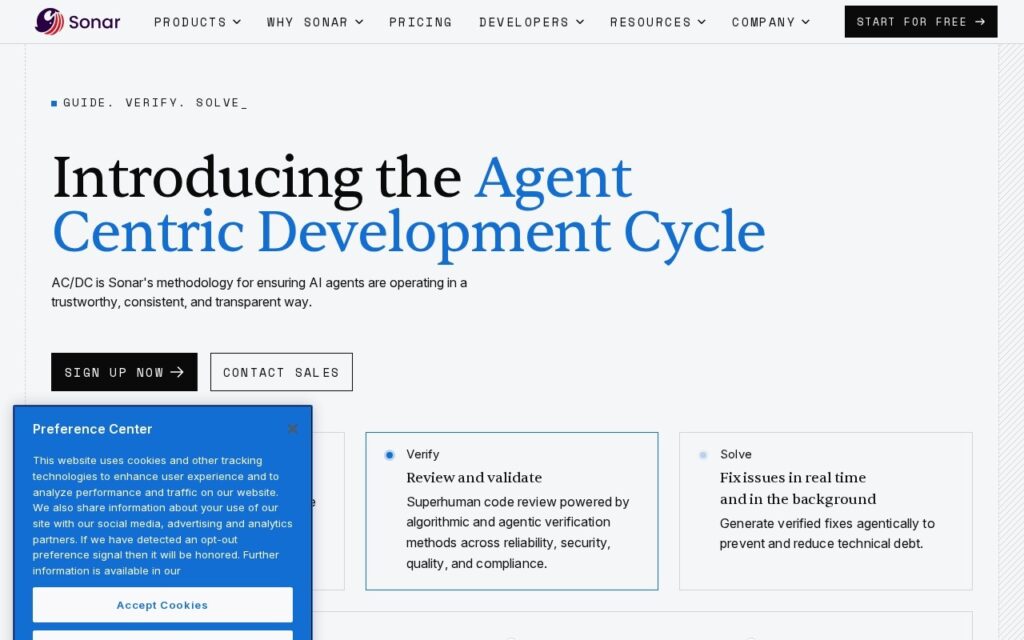
Sonar organizes this around what it calls the Agent Centric Development Cycle (AC/DC) – Guide (provide agents context and constraints), Verify (validate what they produce), Solve (fix issues) – which is a genuinely different governance model than just running one generic AI code reviewer. A measured 3.2% false positive rate matters specifically because autonomous agents that flag too many false issues quickly get ignored by developers; low false positives are what make autonomous remediation actually trustworthy enough to merge without a full human re-review every time.
Sonar Vortex provides the underlying AI agent framework, supplying context and real-time verification during code generation itself, with native integrations into Claude Code, Cursor, Devin, and GitHub Copilot. Beyond the AI layer, Sonar covers 40+ languages, SAST/SCA, secrets detection, and supply chain security, in both cloud and self-managed server configurations. A free tier is available; full pricing requires visiting the dedicated plans page.